Why Antivirus Protection Isn’t Enough.
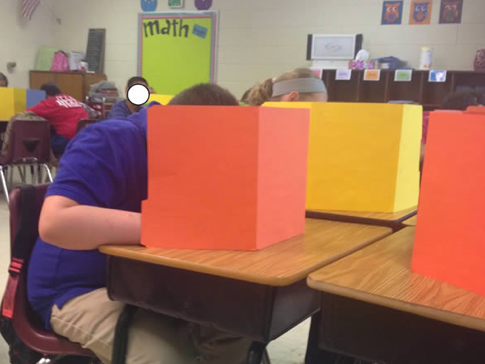
As young students, when we didn’t want someone cheating off of our tests or papers, we put up a folder or Trapper Keeper as a barrier on our desk. This worked great unless someone stood up alleging that they had to use the bathroom. That scoundrel* then had the opportunity to peek over the makeshift boundary.
This is a lot like antivirus software. Minus the bathroom part.
Because of the evolution of cyber threats, like our folder barricades, antivirus software no longer offers the same protection it did in the ‘90s. Not only is cybercrime expanding, attackers themselves are becoming much more sophisticated.
Sophistication isn’t to say that these hackers are solely after large entities, like Equifax or the Democratic National Committee—it’s actually easier for them to target small- to medium-sized businesses (SMBs), and even easier to aim for individuals because every machine that’s connected to the Internet is at risk. Because not all computers are connected through secure servers, antivirus is still the basic security mechanism that every machine should have. It can still keep us safe to a certain extent.
Antivirus fights against malware and can detect suspicious behavior. But it doesn’t hold up as well to sneakier types of malware like ZACCESS, which performs its routines hidden from plain sight.
Also, according to a Popular Science interview with security experts, it’s not enough to just have antivirus software—it must be up to date. Threat information is often found in regular updates and, without that info, the software can’t fight against a potential threat. While IT departments or managed service providers (should) urge everyone in an organization to install regular updates, not everyone follows through.
No matter how up-to-date your software is, though—or how in tune your IT department is—if just one person in your organization downloads an infected file or clicks a harmful link, your security is compromised. Even if you get lucky and none of your employees ever click a link, hackers can often disable antivirus software and other computer security controls anyway.
For signs that your antivirus software has been compromised, check out our blog post “How Do I Know If I’ve Been Hacked?”
If malicious software, or malware, does get through, antivirus software might not be able to detect it. Antivirus software isn’t exactly keeping up with malware’s pace. Antivirus relies on signature detection, which is created by cybersecurity companies after analyzing a new type of malware, but (due to innovation and sophistication) malware changes so rapidly now that the software is using outdated signatures to scan for threats.
While it’s important to start with antivirus software, it’s even more important to understand that additional security measures must be in place.
To find out how you can be sure your organization’s security isn’t stuck in the ‘90s, download our whitepaper, Top Security Trends Propelling Managed SIEM and Managed Detection and Response.
*If you were that scoundrel, this article is not for you.